Cryptocurrency Prices by Coinlib
Phishing App 'SKR Declare' Spent An Hour In Solana DApp Retailer Highlight After Publishing Portal Intrusion – EGamers.io – P2E NFT Video games Portal

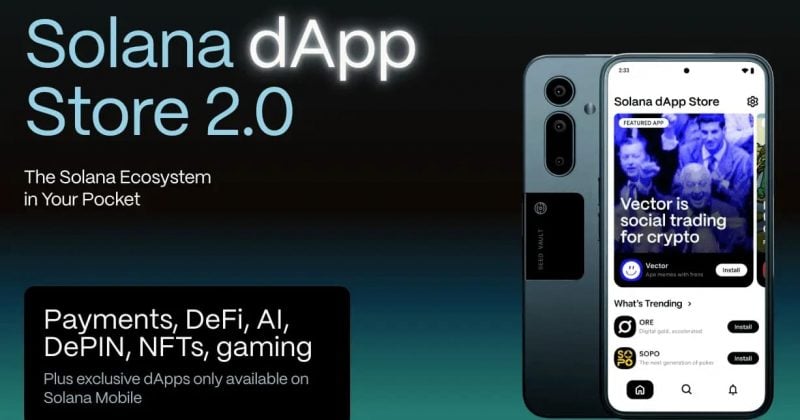
Get our tales first on GoogleAdd egamers.io as a most well-liked supply and our reporting reveals up larger in your Prime Tales.In Transient:An unauthorized get together received into Solana Cellular’s dApp Publishing Portal, and on Nov. 1 a malicious third-party app referred to as “SKR Declare” was submitted to the Solana dApp Retailer, the corporate stated.SKR Declare prompted customers to sort of their seed phrases. It ran within the dApp Highlight for one hour earlier than Solana Cellular pulled it.Solana Cellular stated it mounted the bug that allowed hyperlinks to succeed in apps that weren’t absolutely revealed, and it's eradicating the app from units that put in it.Based on Solana Cellular, a phishing app asking for seed phrases held a spot within the Solana dApp Retailer’s Highlight for an hour on Nov. 1. The shop’s publishing portal had been accessed by somebody with out authorization.The corporate posted about it on X by means of its Seeker account: “At the moment a malicious third get together app named ‘SKR Declare’ was submitted to the Solana dApp Retailer. The App Highlight and Quests UI have been up to date following unauthorized entry to the dApp Publishing Portal. The app requested entry of consumer seed phrases.”At the moment a malicious third get together app named “SKR Declare” was submitted to the Solana dApp Retailer. The App Highlight and Quests UI have been up to date following unauthorized entry to the dApp Publishing Portal. The app requested entry of consumer seed phrases.The app was stay on the dAppThe firm added: “The app was stay on the dApp Highlight for one hour earlier than being eliminated.”How the app received inSubmitting an app was solely a part of what the intruder did. Solana Cellular stated the attacker additionally edited the App Highlight and Quests interfaces, that are the sections of the shop that promote apps and duties to Seeker house owners.Solana Cellular stated it has mounted a vulnerability that allowed hyperlinks to level to apps that hadn’t completed being revealed within the retailer. Due to that flaw, SKR Declare appeared within the Highlight earlier than it had cleared publication.The corporate hasn’t defined how the attacker received entry to the portal.Seed Vault wasn’t touchedSeed Vault, the Seeker’s key storage, was not breached. It holds pockets keys individually from Android and from each put in app, and every signature wants the consumer’s approval by password or biometrics. Non-public keys by no means go away it.SKR Declare made no try and get previous these protections. It requested individuals to enter their seed phrase into the app manually, so it by no means despatched the vault a request.Cleanup is ongoingSolana Cellular stated it's eradicating the app from the units that put in it. It hasn’t confirmed that the elimination is full.No set up figures have been revealed. The corporate additionally hasn’t stated whether or not any consumer entered a seed phrase or misplaced funds.Based on Solana Cellular, its crew won't ever ask customers for a seed phrase or for crypto. It additionally received’t ask them to attach a pockets to different apps or websites to say airdrops.Taking the app off a cellphone does nothing for a phrase that has already been entered. Anybody who typed one in ought to deal with that pockets as compromised, arrange a brand new pockets with a contemporary restoration phrase and transfer no matter belongings stay instantly.Why the ‘SKR Declare’ identify workedSKR is the native token of the Solana Cellular ecosystem, used for governance and staking. Its first distribution passed off in January 2026.For that airdrop, Seeker house owners have been advised to say by means of the cellphone’s built-in Seed Vault Pockets as an alternative of a separate app. The pretend app used the token’s identify and held a high spot within the official retailer’s Highlight for 60 minutes.
Source link